Everything We Need to Know About the AI Act
The European Artificial Intelligence Act is already in force, though it is being applied in stages until August 2027. As of 1 August 2024, the provisions that establish the institutional framework for enforcing the law took effect, including the creation of national supervisory authorities and the European Artificial Intelligence Board.
The Act sets out risk-based guidance for providers and deployers of artificial-intelligence systems and general-purpose models as they relate to specific AI applications.
The Act's core objective is to "promote the uptake of human-centric and trustworthy AI while ensuring a high level of protection of health, safety and fundamental rights." In other words, the Act aims to guarantee safety and protect our fundamental human rights while supporting the adoption of AI in our everyday lives and stimulating investment and innovation within the EU.
The Act also seeks to safeguard the internal market by prohibiting the introduction and distribution of AI products and systems that harm citizens' health, safety, or fundamental rights. Although the Act's emphasis is on a high level of protection for health and fundamental rights, it also aims to encourage innovation and growth among Europe's start-ups. The Act creates a legal framework that allows corporations to develop and test general-purpose models before placing them on the market.
By adopting the AI Act, the European Commission aims to assure citizens that the artificial-intelligence systems operating within the European Union are safe and do not infringe their fundamental rights. The framework is intended to provide citizens with the legal clarity needed to encourage the widespread adoption of AI systems. This combination of trust, security, and clarity is expected to foster innovation and a fuller integration of artificial intelligence into Europeans' daily lives.
A risk-based approach
The European regulation establishes risk-based rules, defining four levels of risk for AI systems:
-
Unacceptable risk - practices that are completely prohibited.
-
High risk - subject to strict requirements and regulatory obligations.
-
Limited risk - requiring transparency in deployment and use.
-
Minimal or no risk - not regulated by the regulation.
Prohibited practices include manipulative techniques or subliminal cues used to alter people's behavior in ways that cause harm. The prohibited category also covers practices involving social scoring and the ranking of people based on behavior, personality, or biometric data, leading to unfair treatment. Biometric categorization on sensitive grounds, the harvesting of facial images without consent, and emotion recognition in the workplace and in education also fall within the scope of prohibited practices.
The next level of risk defined in the AI Act is high-risk systems. The main sectors for high-risk systems are critical infrastructure, education and vocational training, labor and employment, biometrics and identification, access to essential public and private services, law enforcement, migration, asylum and border control, and justice and democratic processes.
Critical infrastructure covers AI that manages systems in infrastructure on which safety and health depend. Justice and democratic processes cover AI used by courts or institutions that assist in decisions on residence permits, asylum, and border crossing. Law enforcement covers AI used by the police, prosecution, or investigative bodies that can restrict rights.
Next come limited-risk systems, which are divided into three subcategories. First are AI systems that people interact with directly, such as the familiar chatbots. Limited risk also covers AI systems for emotion recognition or biometric categorization, as well as systems that people use to generate content, the so-called deepfake systems.
The distinctive feature of this type of AI is that the transparency standards must always be met: when this type of AI is used, it must be clearly indicated that there is interaction with AI or that the content was AI-generated. For example, content (images) created or modified by AI must be explicitly labeled as such so that users can recognize it when they come across it. The same applies when communicating with an artificial-intelligence chatbot.
Last are AI systems deemed to pose minimal or no risk, such as autocorrect tools for writing, AI in video games, and the like. In practice, around 90% of the AI systems in widespread use fall outside the scope of the AI Act. The AI Act does not provide a special regulatory framework for them, and they are left outside its scope. Even so, providers are encouraged to comply with codes of conduct for the voluntary application of some or all of the requirements for high-risk AI systems, which are currently being developed as harmonized standards by JTC21 CEN-CENELEC.
General-purpose AI (GPAI) models
When it comes to general-purpose models, the so-called GPAI (general-purpose AI) models, the Act introduces specific requirements and controls. The Act defines them as models that are:
-
trained on a large amount of data;
-
general in nature, capable of handling a diverse range of tasks;
-
and capable of being integrated into multiple downstream applications.
For providers of such models, the Act sets out both technical and legal compliance rules, such as keeping technical documentation up to date, adopting a policy to comply with the EU Copyright Directive, publicly disclosing a sufficiently detailed summary of the model's training data, and more.
Additional, more stringent rules are established for providers of general-purpose models with systemic risk. These are models with a significant impact on the Union market due to their reach, or due to their actual or reasonably foreseeable negative effects on public health, safety, public security, or fundamental rights, as well as models with significant computational power.
Providers of such models are required to carry out a comprehensive evaluation of the model, including conducting and documenting adversarial testing, to ensure its robustness and reliability under various conditions of use. They must mitigate systemic risks, including their possible sources, by applying measures that reduce the likelihood of negative consequences for citizens' safety, security, or fundamental rights.
In addition, providers must carry out continuous monitoring, documentation, and immediate reporting of serious incidents to the AI Office, enabling a timely response and effective oversight by the competent authorities. Providers are also obliged to ensure an adequate level of cybersecurity for both the model and its associated physical infrastructure, in order to prevent misuse and protect against external attacks.
Conclusion
The AI Act outlines an inherently innovative yet tightly structured framework that places significant obligations on the developers, providers, and users of AI systems. These obligations aim not only to guarantee the protection of fundamental rights and public trust, but also to create legal certainty and predictability in a rapidly evolving technological environment. Successfully implementing the Act will require both technical adaptation and legal compliance from market participants.
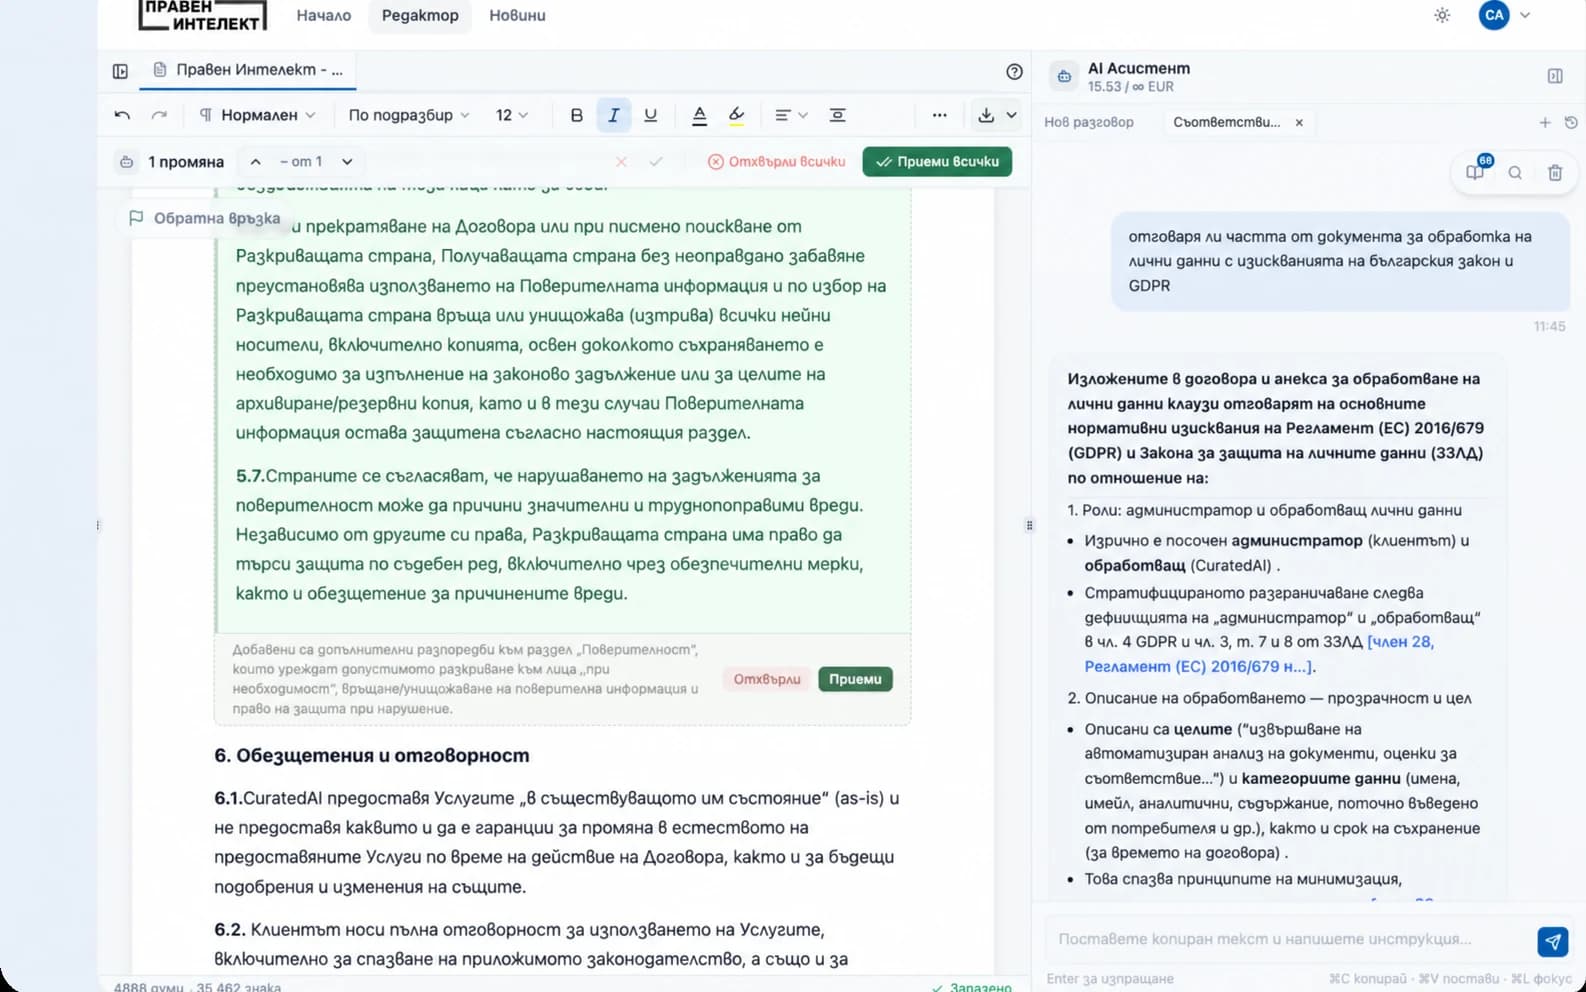
In this respect, tools such as Praven Intelekt can help provide a broader and more precise understanding of the European and national rules in this area, and thereby prevent unlawful conduct by developers and deployers stemming from a misunderstanding of the legal texts.
This article was written by Magdalena Georgieva for VOYCE.